Product Demo
August 17, 2026
Duration: 00:39
Detecting Threats Demo: Monitor, Detect and Remediate a Microsoft 365 Attack
Register to watch


Ransomware doesn't always announce itself.
It moves quietly, corrupts data in the background, and by the time you notice, the damage is already done.
Watch a Veeam Field CTO for a ransomware attack simulation against a Microsoft 365 environment. We’ll demonstrate how Veeam’s AI-driven anomaly detection catches threats at the earliest possible stage, and how teams can act quickly to mitigate the impact before critical data is lost.
In this session, you will:
- Witness a live ransomware attack simulation targeting Microsoft 365 data
- See how Veeam Data Cloud uses behavioral profiling and machine learning to detect threats within backups, without impacting production workloads
- Explore the Veeam Threat Center, which is a centralized hub for ransomware and malware alerts that gives your team a single place to act fast
- Learn how to stop attacks sooner and recover confidently to protect your data, reputation, and bottom line
Speaker
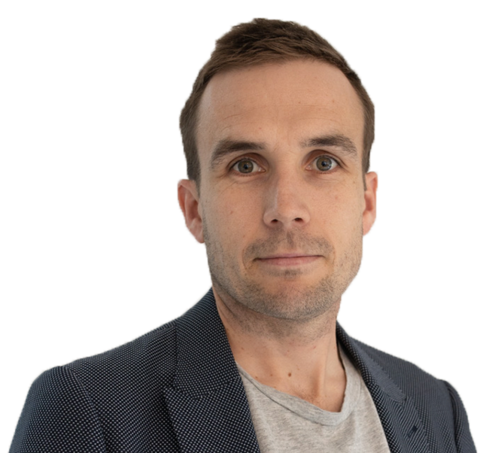
Ben Young
Field CTO APJ, Veeam Software
Field CTO APJ, Veeam Software
Specialising in the integration & automation of a broad range of cloud & virtualisation technologies including Veeam, VMware, Fortinet, Dell EMC into multi-tenant web applications.