- Veeam Support Knowledge Base
- Member servers are not able to authenticate to the Domain Controller
Member servers are not able to authenticate to the Domain Controller
| KB ID: | 1281 |
| Product: |
Veeam Backup & Replication Veeam Agent for Microsoft Windows Veeam Cloud Connect |
| Published: | 2011-10-06 |
| Last Modified: | 2026-10-05 |

Cheers for trusting us with the spot in your mailbox!
Now you’re less likely to miss what’s been brewing in our knowledge base with this weekly digest

Oops! Something went wrong.
Please, try again later.
Challenge
No authority could be contacted for authentication.The trust relationship between this workstation and the primary domain failed.Cause
Solution
Login to the machine using a local (non-domain) account and review the following:
- Verify the trust relationship with the domain by running the following command on the machine.
Test-ComputerSecureChannel -Verbose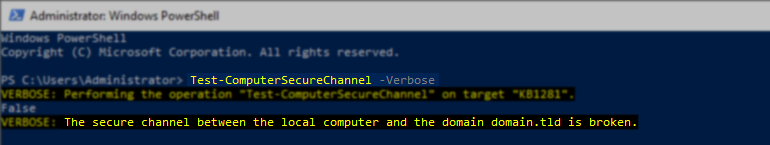
- If the trust relationship is broken, use the following command to repair it.
Test-ComputerSecureChannel -Repair -Verbose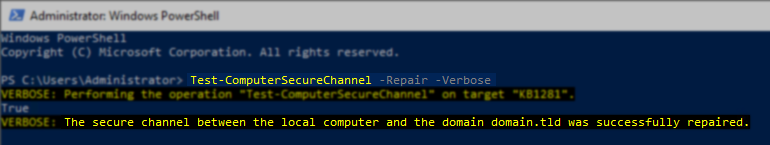
If the repair does not succeed because the current account does not have sufficient permissions in Active Directory, run the command again with the -Credential parameter. When prompted, enter the credentials of a domain account that has permission to reset computer account passwords.
Test-ComputerSecureChannel -Repair -Credential (Get-Credential) -Verbose- Recheck the trust relationship.
Test-ComputerSecureChannel -Verbose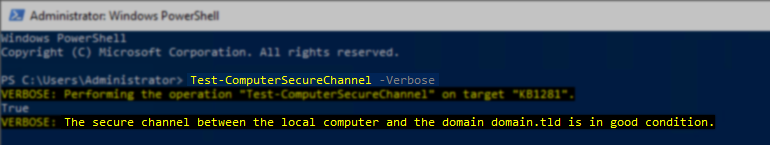
More Information
If domain trust relationship issues continue to occur, it is advisable to investigate the health of the Active Directory servers.
If the repair does not restore the trust relationship, rejoin the machine to the domain, or contact Microsoft Support.
If this KB article did not resolve your issue or you need further assistance with Veeam software, please create a Veeam Support Case.
To submit feedback regarding this article, please click this link: Send Article Feedback
To report a typo on this page, highlight the typo with your mouse and press CTRL + Enter.
