Sign-In Error After Migrating Configuration From MFA-Enabled Server
| KB ID: | 4898 |
| Product: | Veeam Backup & Replication | 13 | 13.1 |
| Published: | 2026-08-10 |
| Last Modified: | 2026-08-10 |


Challenge
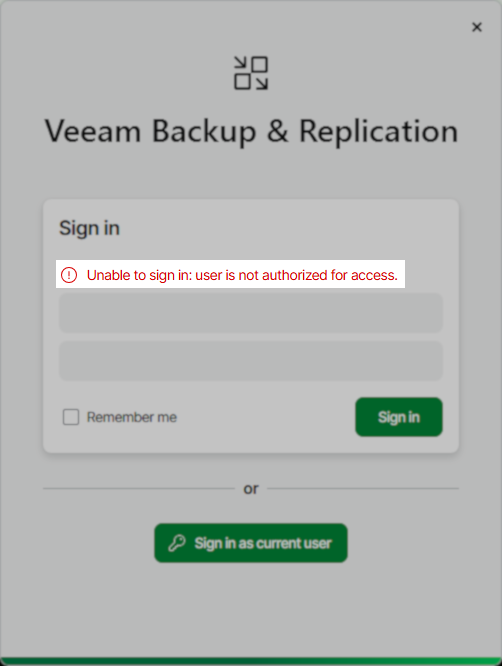
After performing Configuration Restore using the Migration mode from a Configuration Backup created by a Veeam Backup & Replication server that had MFA enabled, login attempts using local accounts cause the Veeam Backup & Replication Console to display the error:
Unable to sign in: user is not authorized for access.
Cause
This issue occurs because the local account being used to log in has no Role assigned within the migrated Configuration Database and therefore has no access. The user accounts, their respective roles, and MFA data are stored within the Configuration Database using the user account's SID. While the local account names between the two machines may be the same, the SID is different and is therefore treated as a user that was never assigned a role.
Note: This same issue will impact domain accounts when migrating the configuration to a machine in a different domain that uses the same domain account names as the initial domain to which the original machine was connected.
Solution
Scenario 1: Migrating to a Machine Joined to the Same Domain
If the configuration was migrated to a machine joined to the same domain as the original Veeam Backup Server:
- Sign in to the Veeam Backup & Replication Console using a domain account that was assigned a Veeam Backup Administrator role.
- Remove the local accounts associated with the old machine from the Users and Roles panel
- (Optional) Add local accounts from the new machine as needed.
Scenario 2: Migrating to a Machine That Is Not in a Domain or Joined to a Different Domain
If the configuration migration was to a machine that is not in a domain or is joined to a different domain than the original Veeam Backup Server, perform the following steps to assign the Veeam Backup Administrator role to the local machine's Administrators user group.
Explanation: On all default deployments, the Administrators user group is assigned the Backup Administrator role. However, when enabling MFA, users are notified to remove all security groups, which results in the Administrators group being removed. After the configuration is restored to the new machine, MFA will be disabled, meaning user groups can be added, but without access to the Veeam Backup & Replication Console the user group must be added via a direct configuration database modification.
- Use the query below to modify the configuration database, assigning the Backup Administrator role to the Administrators user group:
KB1443: How to apply a SQL script to Veeam Backup & Replication/Veeam Backup Enterprise Manager Database
For Microsoft SQL:
- Sign in to the Veeam Backup & Replication Console using an account that is a member of the local Administrators group.
- Open the Users and Roles Security panel.
- Remove Users associated with the old Veeam Backup Server or domain that the machine previously connected to.
- Add accounts as needed and assign their roles.
- If MFA will be enabled again, the
BUILTIN\Administratorsgroup must first be removed from the Users and Roles panel. Before removing the group, confirm that the Backup Administrator role has been assigned to at least one account that is accessible.
Note: Each added account must perform the initial MFA setup steps on the next login.
If this KB article did not resolve your issue or you need further assistance with Veeam software, please create a Veeam Support Case.
To submit feedback regarding this article, please click this link: Send Article Feedback
To report a typo on this page, highlight the typo with your mouse and press CTRL + Enter.
