- Veeam Support Knowledge Base
- How to use "Restore to Amazon EC2" via AWS PrivateLink / Direct Connect
How to use "Restore to Amazon EC2" via AWS PrivateLink / Direct Connect
| KB ID: | 4264 |
| Product: | Veeam Backup & Replication | 13 | 13.1 |
| Published: | 2022-01-20 |
| Last Modified: | 2026-11-10 |

Cheers for trusting us with the spot in your mailbox!
Now you’re less likely to miss what’s been brewing in our knowledge base with this weekly digest

Oops! Something went wrong.
Please, try again later.
Purpose
Solution
Prepare the AWS Environment
- (If using AWS Direct Connect, skip to step 2.)
For AWS PrivateLink, configure a VPN connection to the VPC where you plan to deploy the PrivateLink Endpoint. One of the ways to do this is to create a tunnel on the VM gateway using AWS Client VPN. - Create Endpoints in VPC:
- Create an S3 Interface Endpoint in your VPC. It will be assigned a DNS name that you can see in the AWS Console under VPC - Endpoints when selecting the corresponding Endpoint.
- Create an EC2 Endpoint in your VPC.
Prepare the Veeam Backup & Replication Environment
- Disable automatic updating of the AmazonS3Regions.xml file by creating the following registry value on the Veeam Backup Server.
This will prevent Veeam Backup & Replication from updating and overwriting the changes you'll make in the next section of this guide. Disabling the automatic updating of the cloud regions files also means that when new regions are launched, they will not appear within the Veeam Backup & Replication console.
Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: CloudRegionsDisableUpdate
Value Type: DWORD (32-Bit) Value
Value Data: 1
The 'CloudRegionsDisableUpdate' registry value only disables Veeam Backup & Replication performing its daily check and update of the AmazonS3Regions.xml file.
This registry value does not prevent that file from being overwritten by an updated version of that file contained within and deployed by a product update.
After a product update, the custom changes made in this article must be applied again to the new version of the file. Restoring a saved copy of an older AmazonS3Regions.xml over the new file removes endpoint entries that newer versions of Veeam Backup & Replication require. Keep a record of the custom endpoint values so that they can be entered again.
Step 4 explains how to configure Veeam Backup & Replication to bypass Certificate Revocation List (CRL) checks, which verify if certificates have been revoked by the issuing Certificate Authority (CA). These checks are vital for ensuring only valid certificates are accepted.
Veeam recommends configuring network infrastructure to allow CRL checks whenever possible. However, if the Veeam Backup & Replication server or components lack internet access, disabling CRL checks may be necessary, as outlined in Step 4.
Note that disabling CRL checks affects all Object Storage interactions, not just 'Restore to EC2'. Consider re-enabling this security feature after completing restore operations unless specific needs, like backing up to S3 via PrivateLink or Direct Connect, require it to remain disabled.
- [Optional, Read Note Above] Review the scenarios provided below and, based on whether a Helper Appliance will be used or not, establish the necessary settings to disable certificate revocation checks as advised.
- If Restoring to Amazon EC2 with a Helper Appliance, create the following registry values on the Veeam Backup Server:
- Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: ObjectStorageTlsRevocationCheck
Value Type: DWORD (32-Bit) Value
Value Data: 0 - Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: PublicCloudTlsRevocationCheck
Value Type: DWORD (32-Bit) Value
Value Data: 0
- Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
- If Restoring to Amazon EC2 without a Helper Appliance, the setting must be created on both the Veeam Backup Server and the machine that manages the backup repository data.
Note: We strongly advise using a Helper Appliance for Restore to Amazon EC2 over PrivateLink to eliminate the need to configure custom settings on the repository.
- For Windows-based Repositories, create the following registry value on the Windows machine hosting the repository:
Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: ObjectStorageTlsRevocationCheck
Value Type: DWORD (32-Bit) Value
Value Data: 0 - For Linux-based Repositories (including Hardened Linux Repositories), add the following entry to the /etc/VeeamAgentConfig on the Linux machine hosting the repository:
ObjectStorageTlsRevocationCheck=0
- For SMB Share, NFS Share, Deduplicating Devices (Except ExaGridFor ExaGrid devices Veeam operates a VeeamAgent process directly on the storage operating system. Contact Veeam Support for assistance with configuring the appropriate ObjectStorageTlsRevocationCheck settings. Or, use a helper appliance to bypass the need to modify the repository.), and Object Storage Repositories, the setting must be created on the Gateway server assigned within the respective repositories configuration.
- For Windows-based Gateway servers, create the following registry value:
Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: ObjectStorageTlsRevocationCheck
Value Type: DWORD (32-Bit) Value
Value Data: 0 - For Linux-based Gateway servers, add the following entry to the /etc/VeeamAgentConfig file:
ObjectStorageTlsRevocationCheck=0
- For Windows-based Gateway servers, create the following registry value:
- For Windows-based Repositories, create the following registry value on the Windows machine hosting the repository:
- If Restoring to Amazon EC2 with a Helper Appliance, create the following registry values on the Veeam Backup Server:
- Configure the AWS Appliance to use a Private IP by creating the following registry value on the Veeam Backup Server.
Key Location: HKLM\SOFTWARE\Veeam\Veeam Backup and Replication\
Value Name: AwsApplianceUsePublicIp
Value Type: DWORD (32-Bit) Value
Value Data: 0
Modify the AmazonS3Regions.xml File
The AmazonS3Regions.xml file contains a list of regions and their respective endpoints. Modifying a region's endpoints forces Veeam Backup & Replication to connect to a specific endpoint when that region is selected in the UI. This modification will cause all tasks that utilize the modified region to use the customized S3 and EC2 endpoints.
Each AWS region entry supports only one endpoint configuration. Once a region is configured to use a private connection, public endpoints are no longer available for repositories in that region. Mixing public and private endpoint access for repositories in the same AWS region from a single Veeam Backup & Replication deployment is not supported.
Starting with Veeam Backup & Replication 13.1, each AWS region entry in the AmazonS3Regions.xml file includes an <Endpoint Type="SecretsManager"> line. This line must remain in the region entry that is modified. If it is missing, Restore to Amazon EC2 with a proxy appliance in that region fails with the following error:
Selected data center region does not support SecretsManager endpoints.
The line is missing when an AmazonS3Regions.xml file saved before Veeam Backup & Replication 13.1 is restored, or when the line is removed while editing the file.
- On the Veeam Backup Server, edit the AmazonS3Regions.xml file.
- For Windows-based Veeam Backup & Replication Deployments, this file can be found in:
C:\Program Files\Veeam\Backup and Replication\Backup\AmazonS3Regions.xml
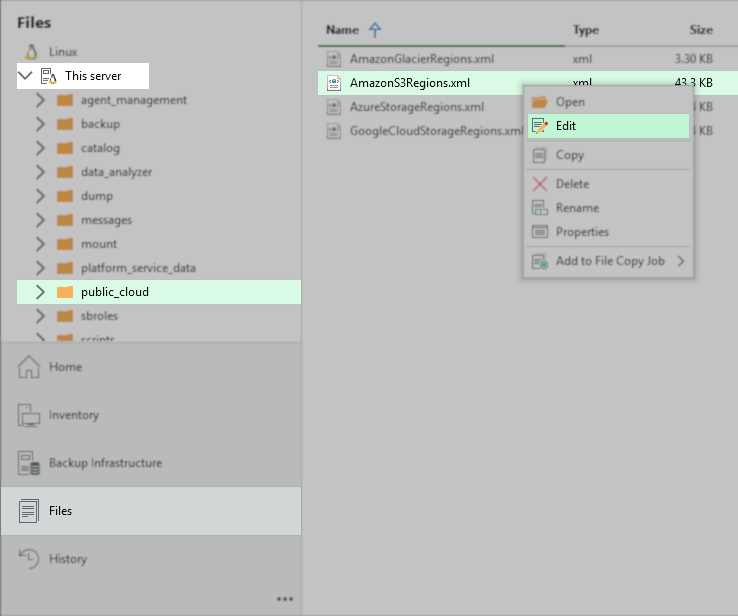
- For Veeam Software Appliance (Veeam Backup & Replication on Linux), use the Files view to locate the file within:
Linux > This server > public_cloud > AmazonS3Regions.xml
- For Windows-based Veeam Backup & Replication Deployments, this file can be found in:
- Find the Region with the "Region ID=" value that matches the actual AWS region of your S3 bucket. For example, if your VPC endpoint serves buckets in us-east-1, you must modify the us-east-1 entry.
Using a mismatched Region ID will result in an AuthorizationHeaderMalformed error from AWS.
Example:
<Region Id="us-east-1" Name="US East (N. Virginia)" Type="Global">
- Within that region's section, find the line <Endpoint Type="S3"> and replace the existing DNS value with the S3 Interface Endpoint DNS created in Prepare the AWS Environment > Step 2.
Note: For S3, the AWS console will display a DNS value starting with an asterisk. When altering the AmazonS3Regions file, replace that asterisk with the word bucket.
Example:
<Endpoint Type="S3">s3.amazonaws.com</Endpoint>
Is changed to:
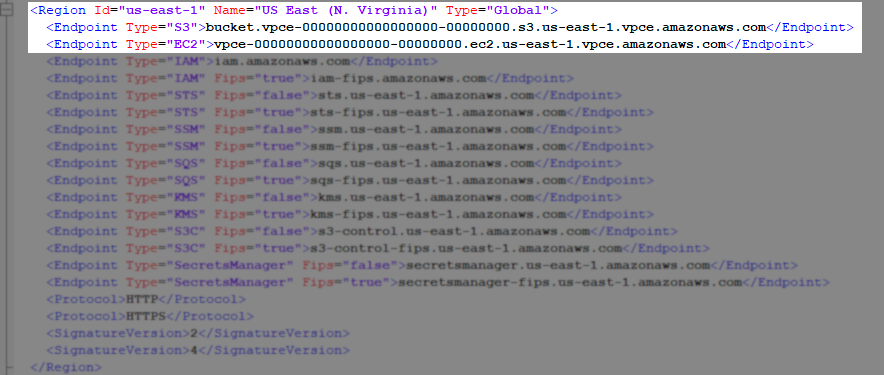
<Endpoint Type="S3">bucket.vpce-00000000000000000-00000000.s3.us-east-1.vpce.amazonaws.com</Endpoint>
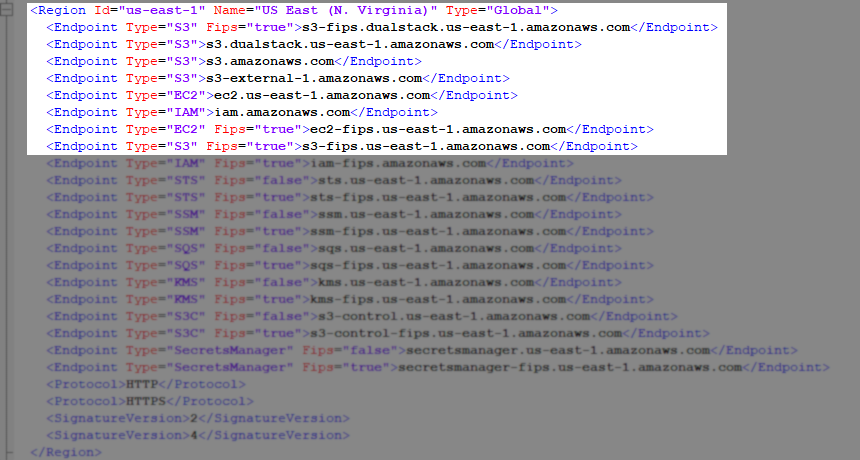
- If multiple lines for <Endpoint Type="S3"> are in the Region section you are altering, remove all but the one you changed. Do not remove or modify
<Endpoint>lines of any other type, including<Endpoint Type="SecretsManager">.
Example:
<Region Id="us-east-1" Name="US East (N. Virginia)" Type="Global">
<Endpoint Type="S3" Fips="true">s3-fips.dualstack.us-east-1.amazonaws.com</Endpoint><Endpoint Type="S3">s3.dualstack.us-east-1.amazonaws.com</Endpoint><Endpoint Type="S3">bucket.vpce-00000000000000000-00000000.s3.us-east-1.vpce.amazonaws.com</Endpoint><Endpoint Type="S3">s3-external-1.amazonaws.com</Endpoint><Endpoint Type="EC2">ec2.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="IAM">iam.amazonaws.com</Endpoint><Endpoint Type="EC2" Fips="true">ec2-fips.us-east-1.amazonaws.com</Endpoint><Endpoint Type="S3" Fips="true">s3-fips.us-east-1.amazonaws.com</Endpoint><Endpoint Type="IAM" Fips="true">iam-fips.amazonaws.com</Endpoint> <Endpoint Type="STS" Fips="false">sts.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="STS" Fips="true">sts-fips.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SSM" Fips="false">ssm.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SSM" Fips="true">ssm-fips.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SQS" Fips="false">sqs.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SQS" Fips="true">sqs-fips.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="KMS" Fips="false">kms.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="KMS" Fips="true">kms-fips.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="S3C" Fips="false">s3-control.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="S3C" Fips="true">s3-control-fips.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SecretsManager" Fips="false">secretsmanager.us-east-1.amazonaws.com</Endpoint> <Endpoint Type="SecretsManager" Fips="true">secretsmanager-fips.us-east-1.amazonaws.com</Endpoint> <Protocol>HTTP</Protocol> <Protocol>HTTPS</Protocol> <SignatureVersion>2</SignatureVersion> <SignatureVersion>4</SignatureVersion> </Region> - Within the same Region section, find the line <Endpoint Type="EC2"> and replace the existing DNS value with the EC2 Endpoint DNS created in Step 2.
Example:
<Endpoint Type="EC2">ec2.us-east-1.amazonaws.com</Endpoint>
Is changed to:
<Endpoint Type="EC2">vpce-00000000000000000-00000000.ec2.us-east-1.vpce.amazonaws.com</Endpoint>
If multiple lines for <Endpoint Type="EC2"> are in the Region section you are altering, remove all but the one you changed. - Save the file.
Perform the Restore
With Veeam Backup & Replication now modified to force it to connect to the specified Endpoints, proceed with performing a Restore to Amazon EC2.
Restore notes:
- When specifying the "Data center region:" select the one that matches the Region you modified in the AmazonS3Regions.xml.
- Enable the "Use the proxy appliance" option.
- If the Veeam Backup server's public internet access is restricted or blocked, when you click 'OK' after you click 'Customize' on the Proxy Appliance step, you may see a warning about "The operation has timed out." Select 'Yes' and proceed.
More Information
If this KB article did not resolve your issue or you need further assistance with Veeam software, please create a Veeam Support Case.
To submit feedback regarding this article, please click this link: Send Article Feedback
To report a typo on this page, highlight the typo with your mouse and press CTRL + Enter.
